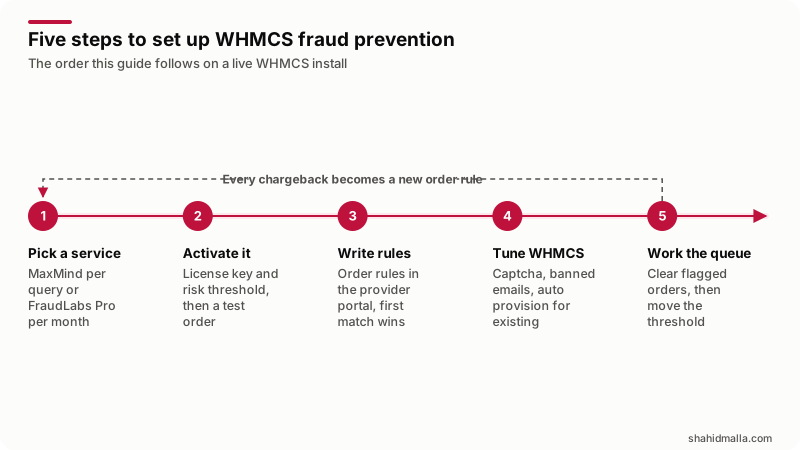
WHMCS fraud prevention lives on one screen, Configuration > System Settings > Fraud Protection, where you activate either FraudLabs Pro or MaxMind. The service scores every client-area order, and anything above the risk threshold you set is marked Fraud before payment is taken. The rules that decide borderline orders sit in the provider's own portal, not in WHMCS.
WHMCS fraud prevention is the set of checks WHMCS runs on a new order before it takes money: a risk score from an outside service, plus the blocks you configure yourself. It does not stop fraud by itself. It sorts orders into the ones you let provision automatically and the ones a person should see first.
Everything below comes from the WHMCS 9.1 documentation and the two vendors' own pages, read on 22 November 2026. The WHMCS documentation home page listed 9.1 as General Availability that day, with 9.0 and 8.13 on Long-Term Support. Prices change.
Which fraud checks does WHMCS already give you?
More than most hosts switch on, and they cost nothing: a captcha on the cart, banned email domains, a custom field that bots fail and the Only Auto Provision for Existing setting that holds automation back for strangers, all on the Spam Orders page.
The paid layer is the fraud module. The Fraud Protection page lists two services and you run one at a time: FraudLabs Pro, which WHMCS marks as recommended, and MaxMind. Both work on self-hosted installs and on the Growth and Expansion plans of WHMCS Cloud.
Two limits shape everything after this. The FraudLabs Pro page says the check runs on new orders customers submit through the Client Area, not on orders admins place in the Admin Area. The Order Management page says WHMCS creates no order record for an automatic renewal that does not involve a new checkout, so a renewal has nothing to score. This is a checkout control, not a continuous one.
Should you run MaxMind or FraudLabs Pro?
Choose on how you want to pay and how much detail you need back. MaxMind bills per query with no minimum; FraudLabs Pro sells monthly plans with a query allowance. minFraud has three tiers, and WHMCS asks you to pick one as the Fraud Check Service Type, priced on MaxMind's plans and pricing page.
| minFraud service | What comes back | Price per query |
|---|---|---|
| Score | Overall risk score, IP risk score, custom inputs and custom rules | $0.005 |
| Insights | Score, plus IP risk reasons and risk data on emails, devices and cards | $0.015 |
| Factors | Insights, plus the risk reasons behind the score | $0.020 |
The same page lists pay-as-you-go billing with no minimums and a free trial of up to 1,000 queries. FraudLabs Pro prices by plan instead, from its pricing page the same day.
| Plan | Per month | Queries a month | Rules |
|---|---|---|---|
| Micro | Free | 500, sales under 25,000 USD a month | 5 |
| Mini | $29.95 | 1,500 | 5 |
| Small | $99.95 | 5,000 | 10 |
| Medium | $249.95 | 25,000 | 20 |
| Large | $499.95 | 100,000 | 30 |
| Enterprise | $1,249.95 | 500,000 | 40 |
The free Micro plan is why FraudLabs Pro suits a young host: 500 checks, five rules and a fraud score at no cost. Paid plans add rules, blacklist entries and checks such as disposable email, which starts at the Small plan. Neither choice is permanent.
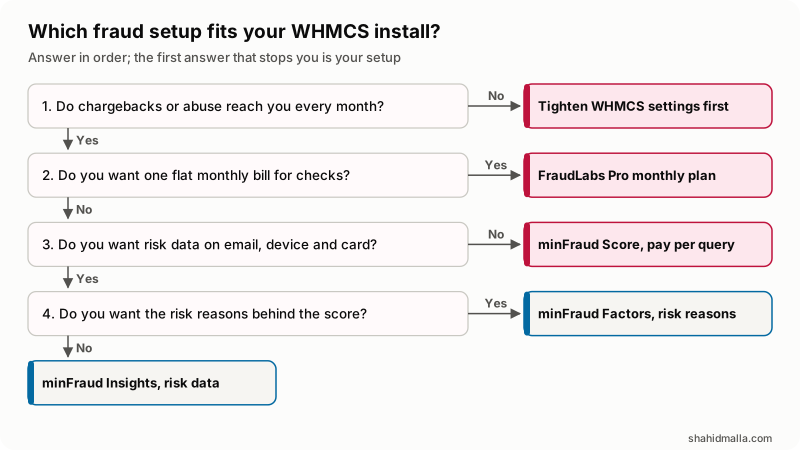
In words: if fraud is not reaching you monthly, tighten the free WHMCS settings and stop there. If it is, and you want one flat bill, take a FraudLabs Pro plan. To pay per order, start at minFraud Score, add Insights for risk data on the email, device and card, and Factors for the risk reasons. Custom rules sit in all three tiers.
How do you turn the fraud module on?
Click Activate on the service you chose at Configuration > System Settings > Fraud Protection, fill in the form and save. The MaxMind page asks for the user ID and license key from My License Key in the MaxMind portal. The FraudLabs Pro page asks for a license key, free to register.
Both then ask for a risk threshold. FraudLabs Pro takes 0 to 100, with 100 the highest risk, and defaults to 20. MaxMind takes 0.01 to 99.9, defaults to 20, and marks anything above your number as fraudulent, preventing checkout. Entering 0 disables the check, which the documentation advises against.
MaxMind adds four switches that act outside the score. Each rejects a whole category of real customers, so set them deliberately.
| MaxMind option | What it rejects | How I use it |
|---|---|---|
| Reject Free Email Service | Free email domains; MaxMind has categorized more than 31,000, including gmail.com and yahoo.com | Off for consumer sales |
| Reject Country Mismatch | Billing address far from the IP address location | On, expect to clear travelers by hand |
| Reject Anonymous Networks | Orders placed through a proxy or VPN | Careful: hosting buyers use VPNs |
| Reject High Risk Country | Billing or IP country MaxMind flags as high risk | Off unless chargebacks say otherwise |
Place one test order through the Client Area after saving. A misconfigured module logs a specific error: INVALID_LICENSE_KEY, LICENSE_REQUIRED, USER_ID_REQUIRED, or MAX_REQUESTS_REACHED when the MaxMind account runs out of queries. That last one lands on a working install months later.
What risk threshold should you actually set?
Start near the default of 20 and move it with evidence. MaxMind's article on setting thresholds for risk scores gives the pattern: accept low scores automatically, for example 5.00 or lower, reject high ones, for example 50.00 and higher, review the rest. Weigh three costs against each other, it says: fraud, manual review, and turning away good orders. The same page publishes a snapshot of how scores fall across all minFraud users.
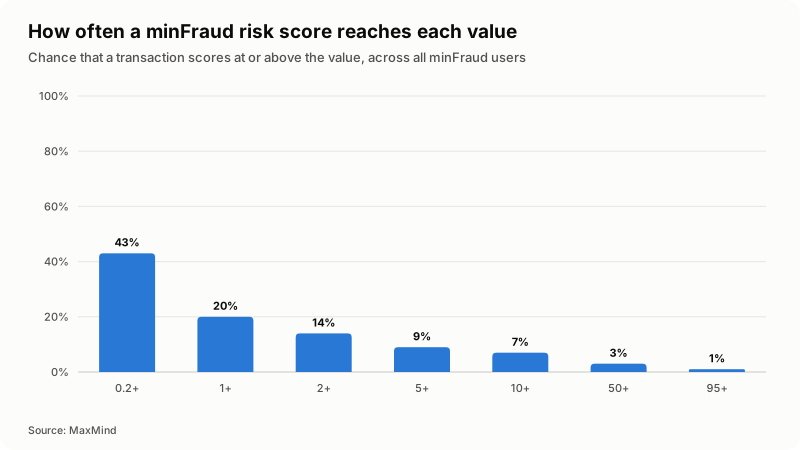
| Risk score | Share of transactions at or above it |
|---|---|
| 0.2+ | 43% |
| 1+ | 20% |
| 2+ | 14% |
| 5+ | 9% |
| 10+ | 7% |
| 50+ | 3% |
| 95+ | 1% |
MaxMind says the distribution varies between users and changes over time, so read it as a shape: a threshold of 50 touches a few orders in a hundred, a threshold of 1 a fifth of them.
Note what WHMCS does with the number: one threshold, two outcomes, pass or Fraud. A middle band for review has to come from a provider rule, from the Only Auto Provision for Existing setting below, or from local rules. I sell a fraud rules and risk scoring module that adds a hold band, so treat that as an interested recommendation.
How do you write order rules for your own fraud?
In the provider's portal, not in WHMCS, and the order of the rules decides the result. Both services read rules top to bottom and stop at the first match, so a loose rule placed early quietly cancels every strict rule below it.
MaxMind's custom rules and dispositions flag a transaction as accept, reject, manual review or test. The first match triggers even if it is a test rule, and an account is limited to 150 active rules. One WHMCS detail is easy to miss: the documentation says MaxMind rules using the accept disposition will not affect the order status, so an accept rule does not rescue an order the score already failed.
FraudLabs Pro creates five default validation rules at signup, each with an action of APPROVE, REVIEW or REJECT. Its tutorial for WHMCS says validation runs before the payment process, and that in WHMCS both REVIEW and REJECT cancel the order, mark it Fraud and stop payment. A review action is not a soft hold; the customer sees the order stop. Its page on rule sequence adds that a transaction matching nothing is approved.
Three rules worth writing once you have seen your own fraud:
- A reject rule for the pattern in your last three chargebacks: one product, one country pair, one email style.
- A review rule for your most abusable product, such as a dedicated server ordered minutes after signup.
- On MaxMind, a rule with the test disposition when you are unsure, so you can watch what it would catch before it cancels anything. FraudLabs Pro has no test action.
Rules decay. Last quarter's country pattern may be gone, and the rule now only catches customers.
Which WHMCS settings do the rest of the work?
The free ones, and on a small host they stop more junk than the score does. All sit under Configuration > System Settings.
- Captcha on checkout. WHMCS recommends reCAPTCHA v3 or hCaptcha in the Security tab of General Settings, and says to check Shopping Cart Checkout under Captcha for Select Forms. Enabling the captcha and forgetting that checkbox is the most common half-done setup I find.
- Only Auto Provision for Existing, in the Ordering tab, provisions automatically only for clients who already hold something Active. It removes the prize: a stolen card buys a server that does not turn on.
- Skip Fraud Check for Existing, also in the Ordering tab, skips the paid check for customers with one active order. It saves queries, and it lets a compromised old account order unchecked.
- Banned Emails blocks email domains at signup, and Banned IPs blocks addresses system-wide, with wildcards in the last two blocks.
Before you take real orders again:
- Captcha enabled and ticked for Shopping Cart Checkout.
- Module activated, key saved, one test order placed and scored.
- Threshold written down with the date and the reason.
- Only Auto Provision for Existing on, unless you accept the risk knowingly.
- A named person and a weekday for clearing the Fraud queue.
Against bulk bot traffic, a firewall in front of WHMCS does more than any of this. The documentation names Cloudflare, Amazon CloudFront, Incapsula and KeyCDN without endorsing any. My guide on WHMCS firewall and server hardening covers that layer.
What do you do with an order marked as fraud?
Open it at Orders > List All Orders and read the fraud result in the Order Items list first. Three moves apply: two from the actions on the Order Management page, plus Re-run, a button in the top right that the FraudLabs Pro page documents.
| Action | What WHMCS does |
|---|---|
| Re-run | Runs the fraud check again from the top right of the order, the move after a client corrects their profile |
| Set Back to Pending | Moves the order from Fraud to Pending and sets the related invoice back to Unpaid |
| Set as Fraud | Marks the order Fraud, runs Terminate on any active service in it, and cancels the invoice |
FraudLabs Pro's WHMCS tutorial fills in the customer side: once the order is Pending again, the unpaid invoice reappears in the Client Area and the client pays it from Billing > My Invoices. Say that in the email, or they assume the order is dead.
For automation, the WHMCS API has an OrderFraudCheck action that takes an orderid and returns the module name and status, such as maxmind and Pass. It answers Order ID Not Found or No Active Fraud Module when something is wrong, which makes it a useful health check in a script.
Where does WHMCS fraud prevention stop?
At checkout, and it only knows what the order tells it.
- Identity is not verified. The built-in identity check depended on Validation.com, which discontinued its service on 9 April 2023, and the User Identity Verification page says the related features no longer function. Document checks need a separate product, such as my KYC identity verification module or a provider API.
- A careful fraudster passes. A clean card, a home connection and a matching billing country produce a low score. That is what a review habit and a provisioning delay are for.
- Personal data leaves your server. Email, IP address and billing details go to MaxMind or FraudLabs Pro on every check. MaxMind's article on its legal basis under the GDPR says it acts as either a data processor or a data controller for minFraud, so read its data processing addendum before you write your privacy notice. My WHMCS GDPR setup guide covers the paperwork.
- False positives have a price. Every rejected real customer is lost revenue and a support ticket. Tune for both errors, not only for fewer chargebacks.
Fraud checking also does nothing about what happens after provisioning. Abuse, spam from a new VPS and mining are server problems, which is why a WHMCS security audit looks at the whole path and not the order form alone.
What else do people ask about WHMCS fraud prevention?
What fraud risk score should I set in WHMCS?
Both modules default to 20, which is a sane start. MaxMind's own guidance is to accept scores around 5.00 and under, reject around 50.00 and over, and review the rest. Record the date you change it.
Why does WHMCS mark normal customers as fraud?
Usually one of the MaxMind reject switches rather than the score. Reject Free Email Service flags every gmail.com, yahoo.com and msn.com buyer, and Reject Country Mismatch flags anyone ordering while traveling or on a VPN. Turn the switch off, re-run the check, and judge the score on its own.
How do I accept an order that WHMCS marked as fraud?
Open the order and click Set Back to Pending. WHMCS moves the order and its services to Pending and sets the invoice back to Unpaid, after which the client pays from the Client Area or you capture payment on the invoice. Click Re-run first if their details have changed.
Is MaxMind or FraudLabs Pro cheaper for a small host?
On prices read on 22 November 2026, 500 orders a month cost $2.50 in minFraud Score queries at $0.005 each, while FraudLabs Pro covers 500 queries on its free Micro plan if monthly sales stay under 25,000 USD. Above that ceiling its Mini plan was $29.95 a month for 1,500 queries.
If your order queue is full of orders nobody trusts, I take that work as a WHMCS security audit or as custom WHMCS development, with a free scoping call of about 30 minutes and a written quote within one business day.
Last reviewed 22 November 2026. Disclosure: I sell WHMCS development, security audits and WHMCS modules, including the fraud and KYC modules named above, so I am not neutral. I am CTO at ElySpace, a freelance developer for Marmaids LLC, and founder of WHMCSPilot and MagizAI.